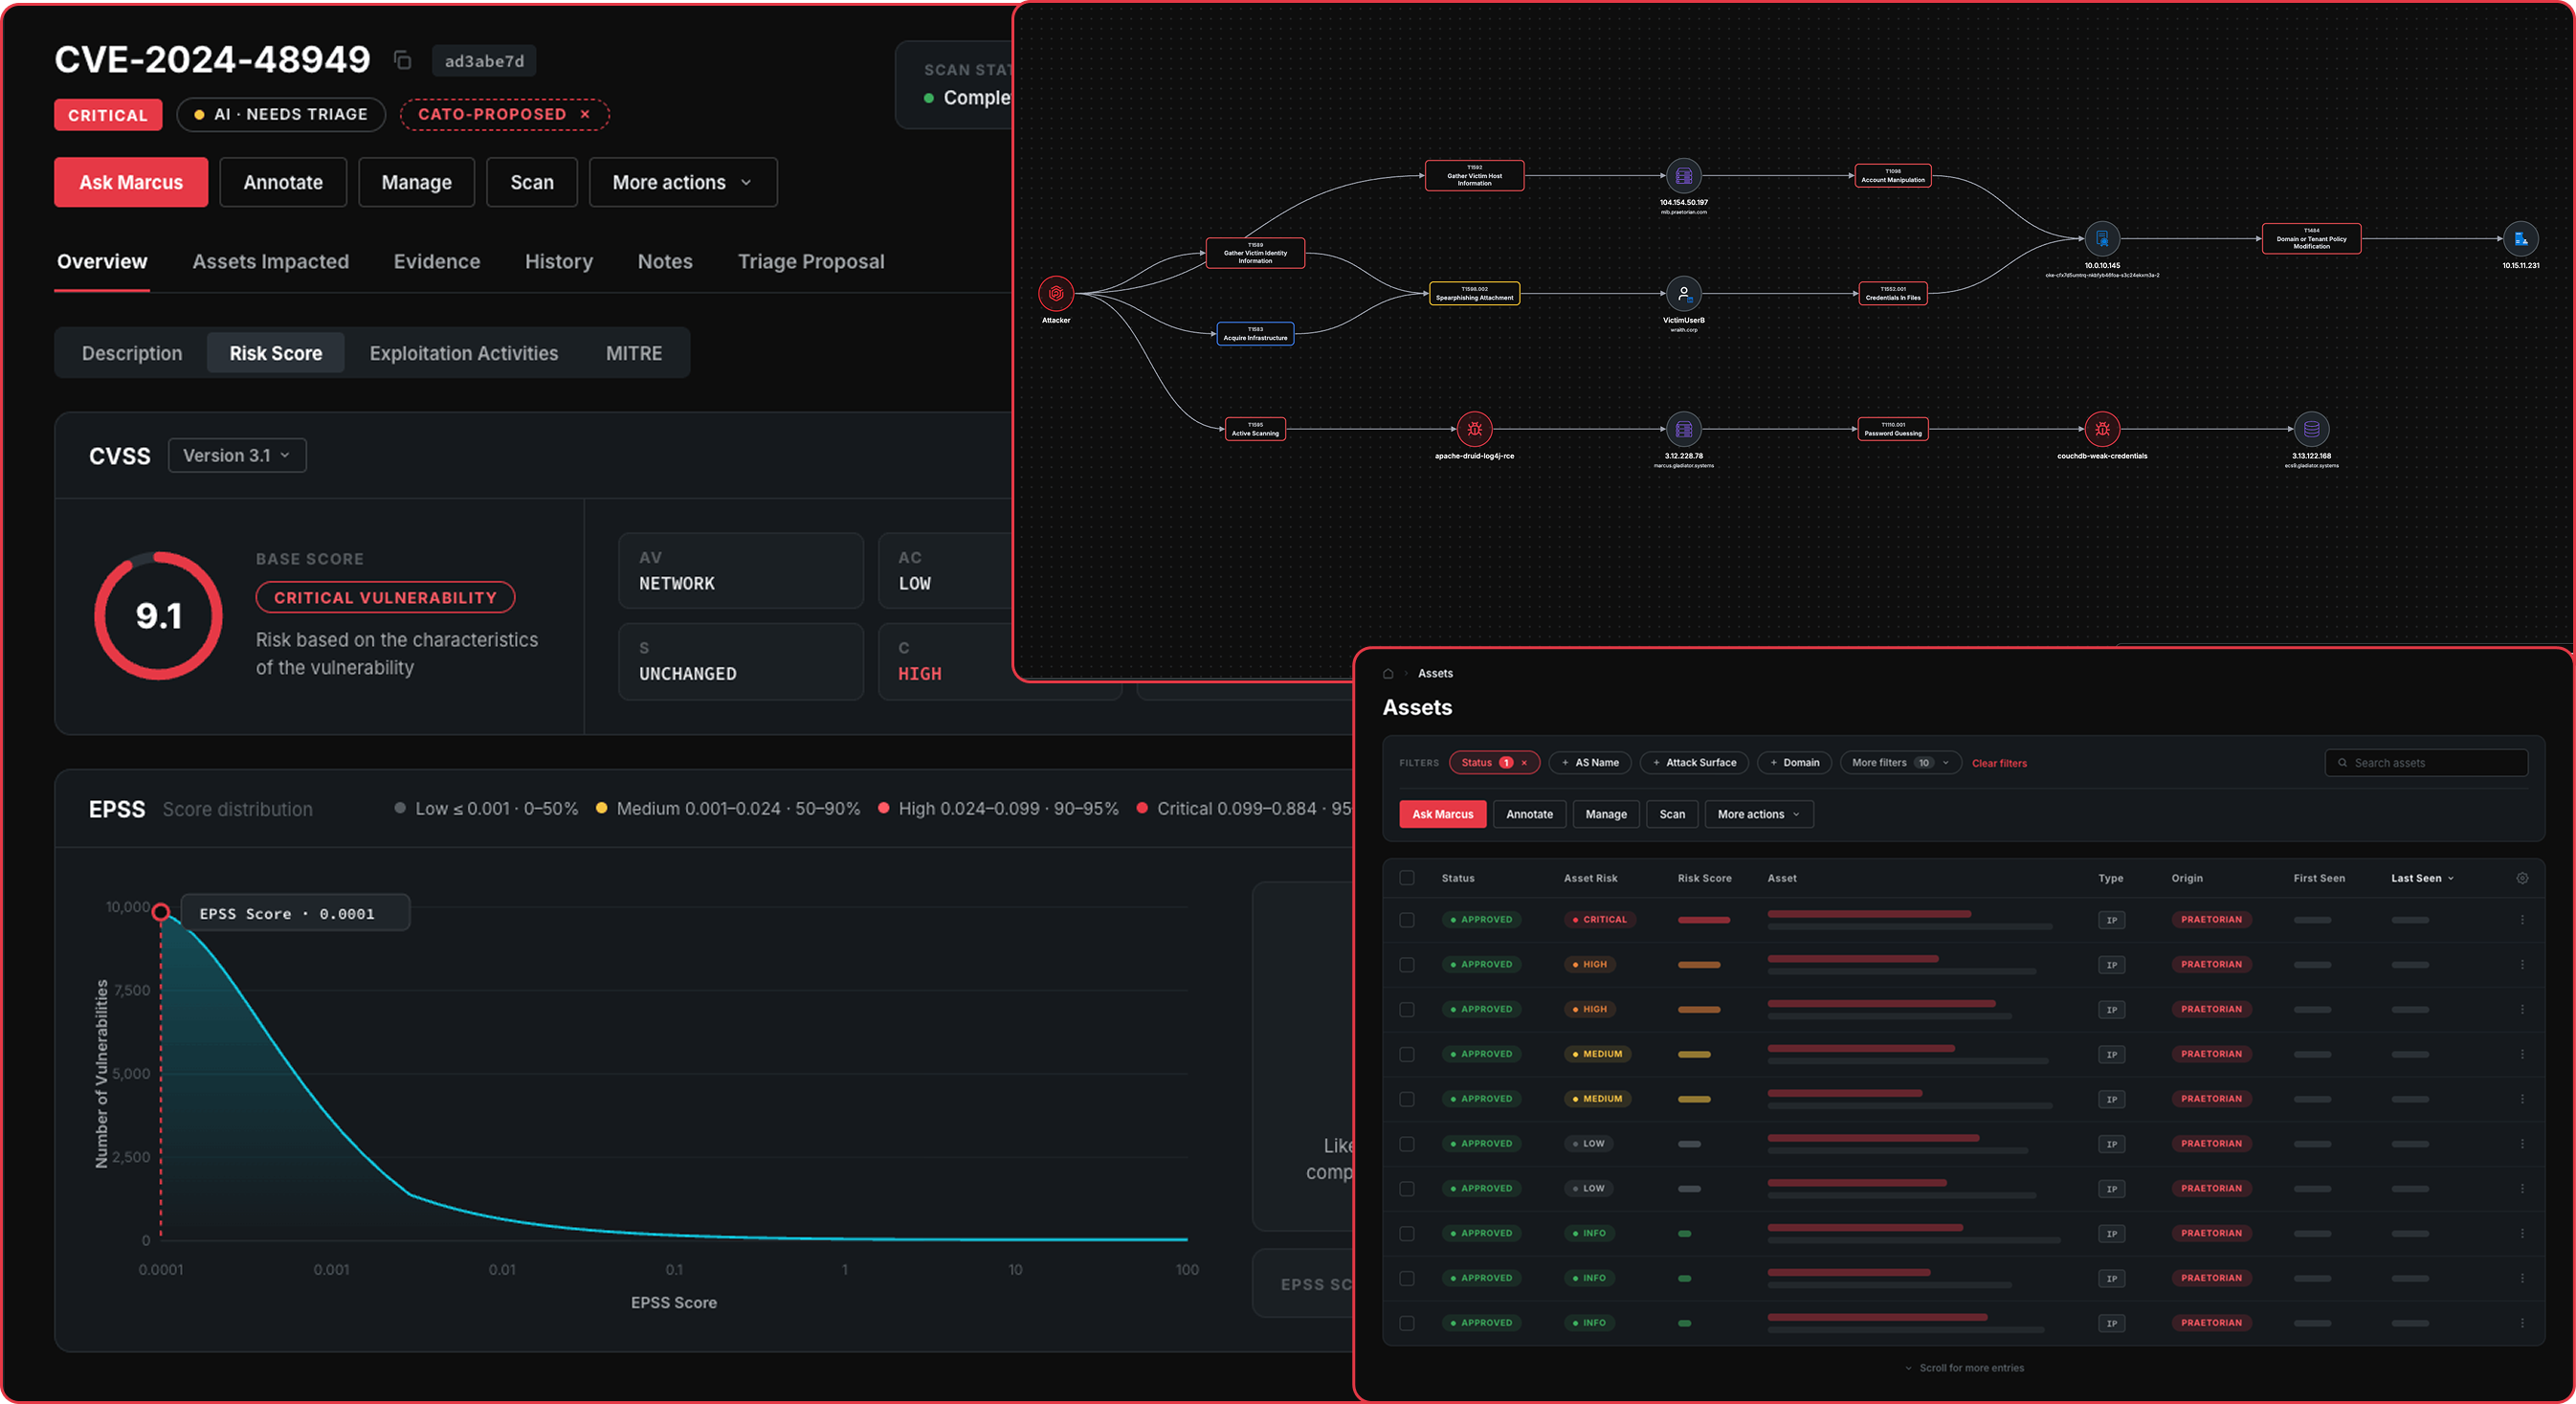
Run offense the way the attacker does. Continuously.
Full platform. No procurement cycle. No sales process.
Get free access
Submit the form. Once approved, your tenant is provisioned within one business day.
Two minutes of Guard. No slides.
Meet Marcus — your conduit into the platform.
Hannibal — fully autonomous offense.
Give Hannibal a mandate and a scope, and it runs the engagement itself, with no human in the loop. Point it at your whole infrastructure or a single newly shipped product; it authenticates (SSO and MFA included), hunts, and reports exploitable risk on whatever cadence you schedule. The default mandate is simple — is it reachable, is it exploitable? — or codify your own: PCI, FDA pre-market, whatever “in scope” means to you. Continuous, autonomous penetration testing that never clocks out.
Offense-Proven Security.
A 35,000 to 1 signal-to-noise ratio
Six categories, unified
The full product. We pick up the tab.
The full platform
Validated, exploitable findings
Free until it proves itself
Getting started takes minutes.
This is the real thing — not a sandbox.
How Guard works — the operator's method, automated.
Map the terrain
Attack every surface
Prove it, then prioritize by impact
Close the loop
Specialized agents, bounded by design.
Zero-day hunting, on demand.
When a target is hard, Guard goes hunting. Constantine reads your codebase, threat-models it, and shards the work across agents so it reasons instead of hallucinates. It doesn't just find the flaw — it writes the exploit, verifies it fires, and can open the patch PR. Its little brother Maxentius operationalizes N-days: the moment a CVE hits CISA KEV, Guard already knows which of your assets are exposed.
Built by the humans who find the zero-days.
Guard is engineered by the operators behind MITRE ATT&CK and CWE contributions, a standing responsible zero-day disclosure program, the Microsoft Bug Bounty Hall of Fame, and a National Counterintelligence Award. The AI scales their craft; it never replaces their judgment.